
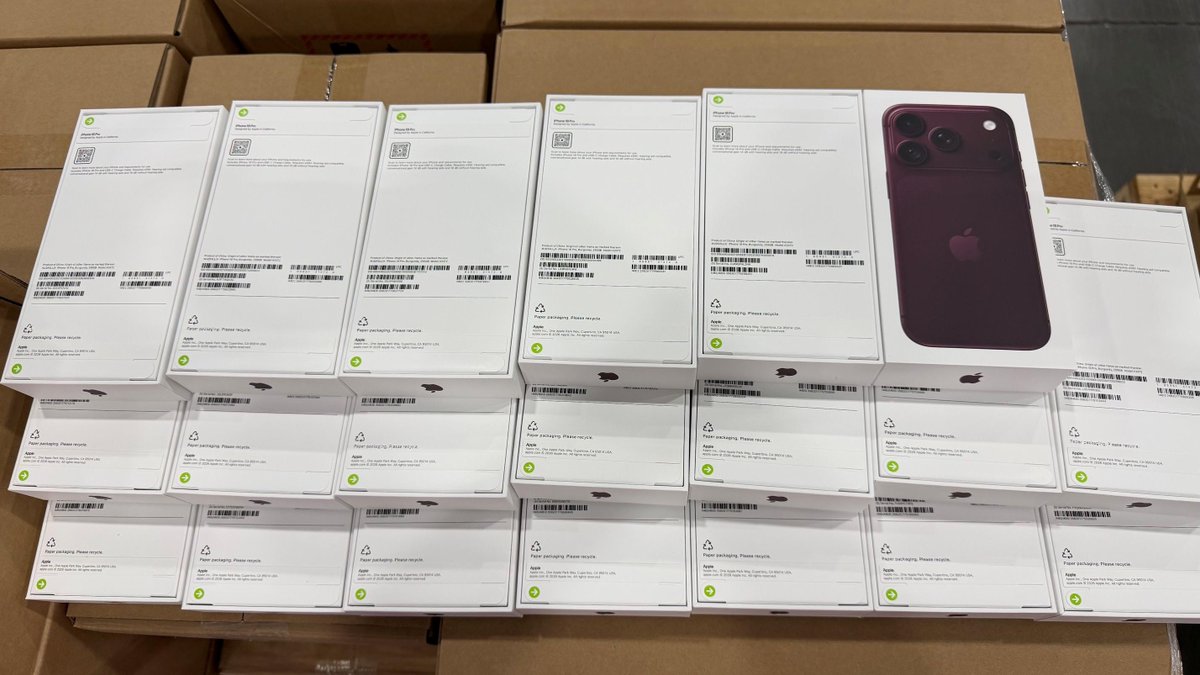
Those IDs are what carriers and Apple use for activation, warranty, inventory, and lost or stolen reports.
With a public IMEI or serial, someone can try to abuse the systems built around those numbers: attempt a fraudulent lost or stolen report, which can get a device blocked from cellular networks, or clone the number onto counterfeit handsets, a known trick that works by copying IMEIs straight off retail packaging.
Source: International Cyber Digest.
This doesn’t surprise me in the slightest. They have a yearly data leak…